
Writing Secure ASP.NET Session (Dutch)
Originally published on my old blog at cumps.be on April 27, 2004.
It has been a long time since I posted something, but here I am again. It’s a very busy time right now, some exams, loads of school tasks, some websites, etc…
And also, a talk I had to prepare for class. One that I’m going to share with you.
I’ll have to disappoint non-Dutch readers though, the slides are written in Dutch, as it was a local session. You could always look at the code though.
The subject was ‘Writing Secure ASP.NET’. Covering:
- Cross-site Scripting
- SQL Injection
- Hashing passwords
- IOPermissions by default
- Unsafe DSN (DSN with password included)
The code for the first three demos should be obvious. Regarding IOPermissions I showed a file browser that could browse through the system in a default ASP.NET installation. And for the Unsafe DSN, I listed system DSNs, or used a demo DSN, showed the tables in it (MySQL only) and executed a query against it.
You can find all files here: SecureASPNET.pdf (197 KB), SecureASPNET.ppt (227 KB) and Demo.zip (205 KB).
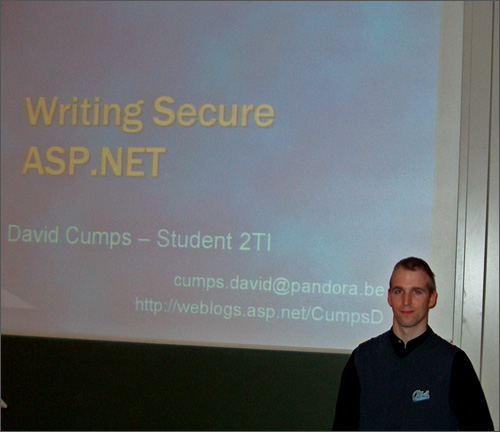
More about this session on the talk page.


You May Also Like

Differences between PHP and ASP.NET
Answers to a forum question for PHP developers moving to ASP.NET with C#: quotes, output, operators, string formatting and arrays.

How This Blog Is Served
The machinery behind the words you're reading: Hugo, an unprivileged nginx, a strict CSP, and a deploy script.

Keeping the Old Addresses Alive
Nobody migrates email in one day. Fetchmail, a receive-only alias domain, and permanent redirects bridge the old world into the new one.